Nepal Rastra Bank Shuts Down Website Over PHP Security Risk
Nepal's central bank suspended its website and related services on Friday as a precaution against the global PHP flaws, and told banks, payment firms and remittance companies to tighten security and watch their systems closely.
Key points
- Nepal Rastra Bank has temporarily shut down its website and related services as a precaution against the serious security flaws found in PHP, the programming language that runs much of the web.
- The bank asked the public to follow its official social media channels for essential notices and information while the website is offline.
- Nepal Rastra Bank also directed the institutions it supervises to act.
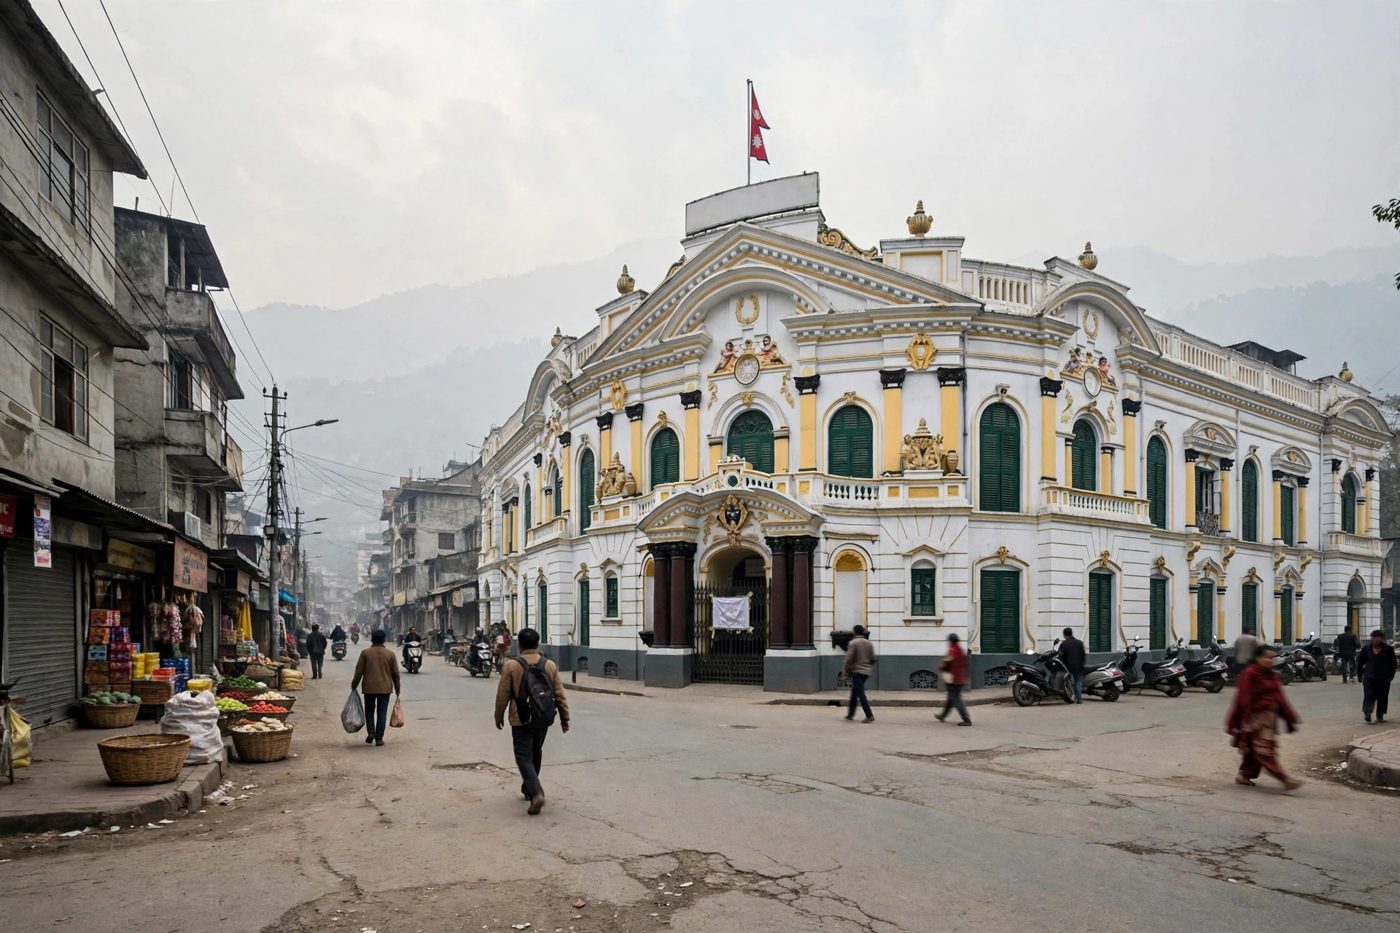
Nepal Rastra Bank has temporarily shut down its website and related services as a precaution against the serious security flaws found in PHP, the programming language that runs much of the web. The central bank announced the move in Kathmandu on Friday, Oct 23, 2026, in an urgent notice that said the step was taken to minimise potential risks that could cause inconvenience to stakeholders in the banking and financial sectors and to the general public.
The bank asked the public to follow its official social media channels for essential notices and information while the website is offline. It gave no time for when the site and services will return.
What the central bank told banks and payment firms
Nepal Rastra Bank also directed the institutions it supervises to act. It urged banks and financial institutions, payment system operators, payment service providers and remittance companies to adopt necessary security measures against potential cyber threats, strengthen the security of their systems and increase regular security monitoring. The notice called on all concerned institutions to give special attention to cybersecurity and risk management and to take the precautions needed to guard against potential threats.
For Nepali families who receive money from relatives working abroad, the remittance part of that list matters most. The central bank named remittance companies directly, which means the firms that move money into Nepal have been told to watch their systems closely while the patch work goes on.
Why a website language flaw reached a central bank
The shutdown follows the disclosure of two critical flaws in PHP, tracked as CVE-2026-109618 and CVE-2026-109619 and known together as PHP2Shell. Both carry a severity score of 9.2 out of 10. PHP runs behind the scenes on servers for sites built on platforms such as WordPress, Drupal and Joomla, and security agencies in the United States and Europe urged operators to install the emergency fixes or take vulnerable sites offline until they could.
PHP developers released fixed versions, PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35, on Oct 21, 2026. Attackers began probing for unpatched servers within hours, which turned the patch into a race for every organisation that runs a public website.
Nepal moved early. Government websites in Nepal were taken offline as a precaution on Oct 22, 2026, after the flaws became public, and reports on Thursday morning said the websites of government offices were inaccessible. The central bank's decision on Friday extends the same precaution to the financial sector's regulator.
What readers should do
The central bank's advice is simple. Get NRB notices only from its official social media channels while the website is down, and treat any message that claims to come from the bank through other channels with care. People who bank or receive remittances in Nepal should use their bank's official app or branch channels for urgent work and expect public web pages to stay offline until the security updates are in place.
Timeline
- Oct 21, 2026PHP developers release emergency fixed versions, PHP 8.5.12, 8.4.27, 8.3.36 and 8.2.35, for two critical flaws scored 9.2 out of 10.
- Oct 22, 2026Government websites in Nepal are taken offline as a precaution after the PHP flaws become public.
- Oct 23, 2026Nepal Rastra Bank suspends its website and related services and urges banks, payment operators and remittance companies to strengthen security and monitoring.
Sources
- Peoples' Review: Nepal Rastra Bank temporarily shuts down website, services over PHP security risk
- ICT Frame: NRB Website Shutdown Global PHP Vulnerability Cybersecurity
- Peoples' Review: Serious security vulnerability discovered in PHP, affecting government websites worldwide, including Nepal
- Reuters: What is PHP, and why did it take government websites offline